Asheville Tax Accountant: Accurate, Compliant, and Cost-Effective Solutions
WRITTEN INFORMATION SECURITY PLAN (WISP)
Ron J. Miller D/B/A All In One Financial Services is a sole proprietor tax preparation, tax and financial consulting firm which has only one practitioner.
IRS EFIN: 569741 | PTIN: P00758919
Said practitioner is also a licensed Life, Health, and Annuity producer in the States of NC & NJ.
National Producer #: 7415336 | NJ License #: 8107759
All In One Financial Services
105 Paper Birch Avenue
Asheville, NC 28806-0007
1. Purpose and Scope
This Written Information Security Plan ("WISP") establishes the administrative, technical, and physical safeguards deployed to protect nonpublic personal financial info and client Personally Identifiable Information (PII). This plan fulfills the mandates of the Federal Trade Commission (FTC) Safeguards Rule under the Gramm-Leach-Bliley Act and IRS Publication 4557/5708 requirements for tax preparation professionals.
Scope: This WISP applies specifically to a sole practitioner operational environment featuring a single desktop computer, on-premise local tax preparation software, and a dedicated non-Wi-Fi, hardwired Ethernet internet connection. No external cloud-hosting platforms or multi-user networks are utilized for core tax data storage.
2. Designated Data Security Coordinator
As a sole practitioner, the principal practitioner acts as the designated Data Security Coordinator. The Coordinator is responsible for executing, maintaining, and reviewing this WISP, performing annual risk assessments, and ensuring compliance with all local security procedures.
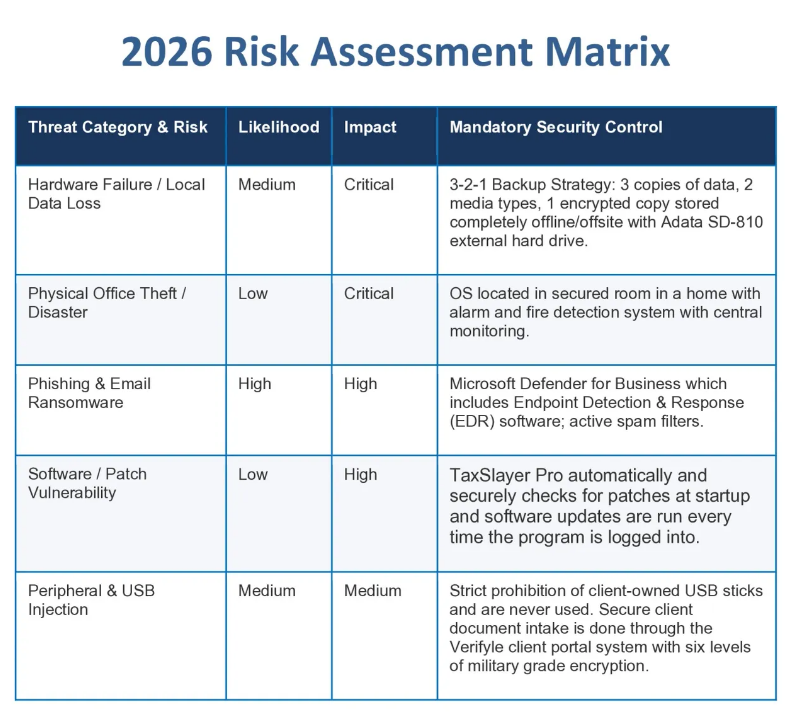
3. 2026 Risk Assessment Matrix
See chart at the bottom of this page.
4. Technical and Administrative Safeguards
4.1 Physical and Environment Controls
- Device Security: The primary desktop workstation hosting the tax data must remain physically secured inside the home office using deadbolt entry controls. It is kept in a separate secured room in a house that has an alarm system with central monitoring.
- Screen Auto-Lock: The workstation must be configured to automatically lock requiring biometric or strong complex password authentication to resume.
- External Media Restrictions: To eliminate external physical threats, client physical flash drives, external hard drives, or media cards are strictly prohibited from connection to the workstation environment.
4.2 Network Controls for Hardwired Environments
- Wi-Fi Deactivation: The wireless adapter interface (Wi-Fi) on the motherboard or internal card must remain permanently disabled via the operating system network control interface.
- Perimeter Security: Internet intake goes exclusively via a physical Ethernet cable attached to a hardware router. The hardware router firewall must remain active, block anonymous incoming ICMP traffic, and change default administrator credentials.
4.3 Endpoint and Software Defenses
- Privilege Restriction: The everyday user profile utilized for client preparation must execute under a non-administrative account. Administrative elevation must require a separate standalone credential.
- Active Protection: The system must maintain an active subscription to a managed Endpoint Detection and Response (EDR) or premium anti-malware system featuring live heuristic file monitoring.
5. Data Breach and Incident Response Plan
In the event of a suspected security event (e.g., malware infection, unauthorized physical access, ransomware window), the Data Security Coordinator will immediately execute the following steps:
- 1Isolation: Physically disconnect the Ethernet cable from the workstation to cut off external communication without powering down (to preserve volatile memory forensics).
- 2Assessment: Identify whether client PII (Personally Identifiable Information) was extracted or rendered unreadable.
- 3Notification: If unencrypted client PII is compromised, contact the local IRS Stakeholder Liaison within 24 hours, alongside state tax authorities and affected clients in accordance with state data breach notifications laws.
- 4Remediation: Clean hardware utilizing full image restoration from clean, offline backup nodes before bringing systems back to production environments.
6. Program Evaluation and Maintenance
This WISP will be reviewed, tested, and updated at least annually or whenever significant alterations occur to the operational environment. The next structured validation window will occur no later than December 31, 2026.
7. Client Portal System
The practitioner subscribes to a client portal system by a third party vendor called VeriFyle which is cloud based. It utilizes six levels of military grade encryption to share documents with PII. Electronic signatures can also be facilitated. All clients are urged to employ the use of the VeriFyle system. For clients' who utilize the provided VeriFyle client portal system will have to adhere to the strict guidelines of passwords established through the VeriFyle system. VeriFyle will not share or distribute password information to anyone or entity. It is the sole responsibility of the client to keep such passwords secure but obtainable for future and continued use. All In One Financial Services, it's heirs or assigns shall not have any access to VeriFyle password information and therefore will be held harmless.
8. Anti-Virus and Vulnerability Management Programs
The firm utilizes Microsoft Defender for Business anti-virus installed on all systems and it is set to automatically update when a new virus definition is released. Systems are set to automatically install updates when they are released. Applications that are used on the systems are set to automatically update and/or the system administrator receives email updates when a new version is available for download.
9. Information Disposal
Proper disposal of digital information by use of media sanitization, clearing, purging, and/or destroying the devices will be followed by All In One Financial Services. This will also be followed for disposing of hard copy information which has PII or customer data on it, such as using a cross-cut shredder.
10. Back-up and Disaster Recovery Plan
Critical data will be periodically backed-up on an "External Hard Drive" and any other means deemed appropriate by the proprietor to secure client data. The current external hard drive is "Adata Model SD-810". The use of the VeriFyle portal system is a back-up system in of itself. Additionally the firm subscribes to Carbonite, which is also an offsite cloud back-up system. These tools would be the means of data recovery in the event of a natural disaster such as storms, hurricanes, or tornadoes.
11. System and Data Inventory
Below is the inventory of the systems and where the data is stored and the type of information which is stored on the system.
- (A)Dell Inspiron 3880 Desktop Computer with Microsoft Defender for Business is the computer system located in the practitioners Home/Office which stores Tax Returns and all related documents provided by clients.
- (B)Microsoft Windows 11 is the main operating system.
- (C)Adata SD-810 external hard drive is used for computer file back-up.
- (D)CyberPower 1500 AVRL CD3 which is an LCD UPS (Uninterruptible Power Supply) system providing battery backup and surge protection while featuring a built-in digital screen to display real-time power vitals like battery capacity, load level, and input/output voltage. My computer, modem and router are all plugged in.
12. Implementation
Effective January 1st, 2026, All In One Financial Services has created this Written Information Security Plan (WISP) in compliance with regulatory rulings regarding implementation of a written data security plan found in the Gramm-Leach-Bliley Act and the Federal Trade Commission Financial Privacy and Safeguards Rules.
Practitioner Signature
Ron J. Miller
Date
January 1st, 2026
3. 2026 Risk Assessment Matrix